Fractional
Chief Information Security Officer
Your holistic Cybersecurity Strategy - taken care of:
Assess → Prioritize → Implement → Empower → Improve
Your CISO as a Service:
Carolin Desirée Toepfer
As external Chief Information Security Officer and IT Forensics Specialist, I help organizations build a stronger cybersecurity posture, adopt AI securely, and turn complex risks into clear, actionable decisions - since 2016.
My work sits at the intersection of Cybersecurity, AI Security, Risk Management, and Regulatory Compliance. I help organizations understand emerging cyber and AI risks, establish practical security structures, and implement secure AI solutions without slowing down innovation.
I sit at the table where the rules are written: as a member of several working groups, I collaborate directly with legal experts, representatives of highly regulated organizations, and relevant authorities. I translate complex regulatory and security requirements into practical, cost-efficient measures that strengthen resilience without creating unnecessary bureaucracy.
As an entrepreneur, I understand the reality behind the requirements. Security needs to work not only on paper, but in everyday operations, under time pressure, with real people, real budgets, and constantly changing technology. My goal is to enable organizations and their teams to make better security decisions every day.
My keynotes and trainings are popular with both executives and employees because I don't use fear to create awareness, and I don't create dependencies to sell security.
Fractional CISO & Cybersecurity Transformation
Turn cybersecurity into your business advantage!
Practical cybersecurity leadership for growing companies that want to strengthen their security posture, meet regulatory requirements and build a resilient organization.
As your external Chief Information Security Officer (CISO), I combine strategic guidance with hands-on implementation. From closing security gaps and establishing an Information Security Management System (ISMS) to preparing for NIS2, DORA and certification requirements, I help you turn cybersecurity into an integral part of your business.
Strategic direction. Practical implementation. Sustainable security.
What I do
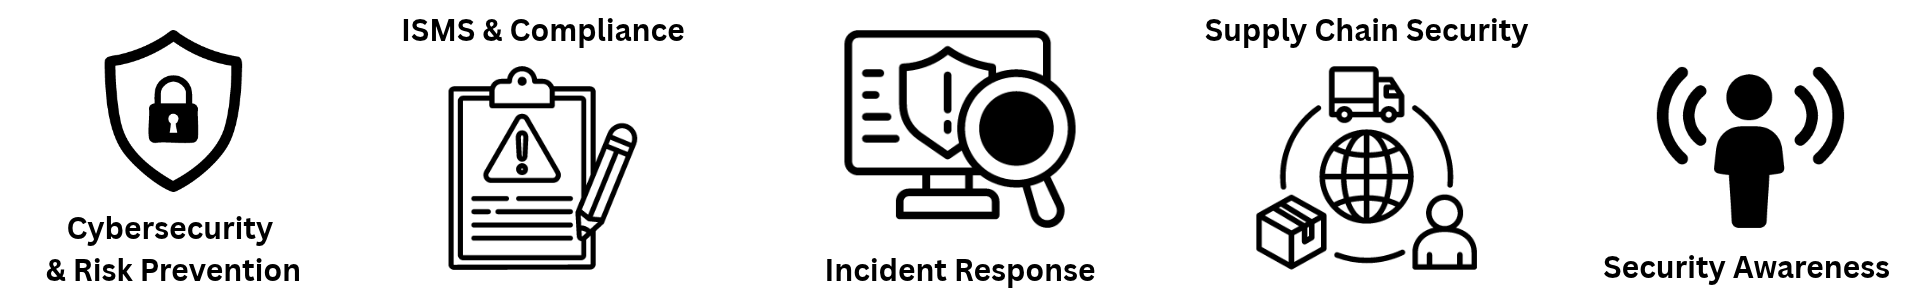
#1 Security Strategy & Risk Management
Build a clear understanding of your security posture and establish a roadmap for improvement.
- IT infrastructure and security assessments
- EU NIS2, DORA, CRA gap analysis
- Risk assessments and risk management frameworks
- Risk matrices and remediation roadmaps
- Technical security quick fixes
- Security strategy and management advisory
#2 ISMS & Regulatory Readiness
Establish the structures, processes and documentation needed for effective information security management.
- ISMS development and implementation
- Security policies and processes
- Incident reporting and ticketing workflows
- Business Continuity Management integration
- Internal audits and compliance reviews
- External audit and certification preparation
#3 Incident Response & Crisis Management
Make sure your organization knows how to respond when things go wrong.
- Incident Response process development
- Security incident reporting procedures
- Incident Response workshops and exercises
- Crisis communication planning
- Roles and responsibilities for security incidents
- Continuous improvement of incident handling
#4 Supply Chain & Third-Party Security
Extend your security standards beyond your own organization.
- Supplier security management
- Third-party risk assessments
- Review of customer security questionnaires
- IT security reviews of supplier contracts
- IT Business Partner Trust Circle
- Collaborative security initiatives with business partners
#5 Security Awareness & Culture
Make cybersecurity everyone's responsibility.
- Employee awareness initiatives
- Security workshops and training
- Cybersecurity communication
- Internal security champions
- Sustainable security culture development
How we work together
Assess. Prioritize. Implement. Empower. Improve.
My approach is pragmatic, risk-based and tailored to your organization's needs.
- Assess — Understand your current security posture, business requirements and regulatory obligations.
- Prioritize — Identify critical risks and define a realistic security roadmap.
- Implement — Establish processes, controls and structures that work in practice.
- Empower — Enable employees, management and business partners to actively contribute to security.
- Improve — Continuously review, measure and strengthen your security maturity.
Why work with an External CISO?
You get experienced cybersecurity leadership without having to build a full-time executive function internally.
- Strategic perspective: Connect cybersecurity with business objectives and risk management.
- Hands-on execution: Move beyond recommendations and turn priorities into actionable measures.
- Regulatory understanding: Address NIS2, DORA and relevant security standards.
- People-centric approach: Build security awareness and internal capabilities.
- Scalable support: Adapt the level of engagement to your company's needs and maturity.
Let's make your organization more resilient.
Whether you are establishing your first ISMS, preparing for regulatory requirements, strengthening your supply chain or looking for ongoing cybersecurity leadership — let's discuss where you are today and what your next steps should be.