From Zero to Cybersecurity Certification
Build a Cybersecurity System your Clients can TRUST!
The 12-week Cybersecurity Boost and long-term Cybersecurity Support Community for Startups and SMEs.
Get clarity on your cyber risks, build the right security foundations, prepare for certification and respond confidently to customer and regulatory requirements.
You don't need to become a cybersecurity expert. You need to know what your company needs to do AND HOW TO GET IT DONE!
What you'll build:
📰 Stay up to date regarding global Attack Scenarios
Receive regular content updates, empowering you to protect your business.
🔎 Know where you stand...
Assess your current cybersecurity level, risks, gaps and priorities.
🗺️ ...and what to do next!
Create a practical cybersecurity roadmap for the next 30, 90 and 365 days.
🛡️ Build your Security Foundation
Establish your risk management, policies, processes, employee security and supplier management.
📁 Create your Evidence
Build the documentation and evidence needed for clients, auditors and certification projects.
🔒 Keep Attackers out...
Maintain a holistic cybersecurity strategy and orchestra of needed measures against cybercrime, digital fraud and AI-driven risks.
🚨 ...yet be ready for Incidents as well!
Create an incident-response and worst-case plan before you actually need it. Define and implement your level of business continuity measures - in time.
🏆 Prepare for Certification
Understand and prepare for ISO 27001, CyberTrust, SOC 2 and relevant regulatory requirements.
💼 Support your Sales
Build a reliable approach to customer security questionnaires and enterprise security requirements.
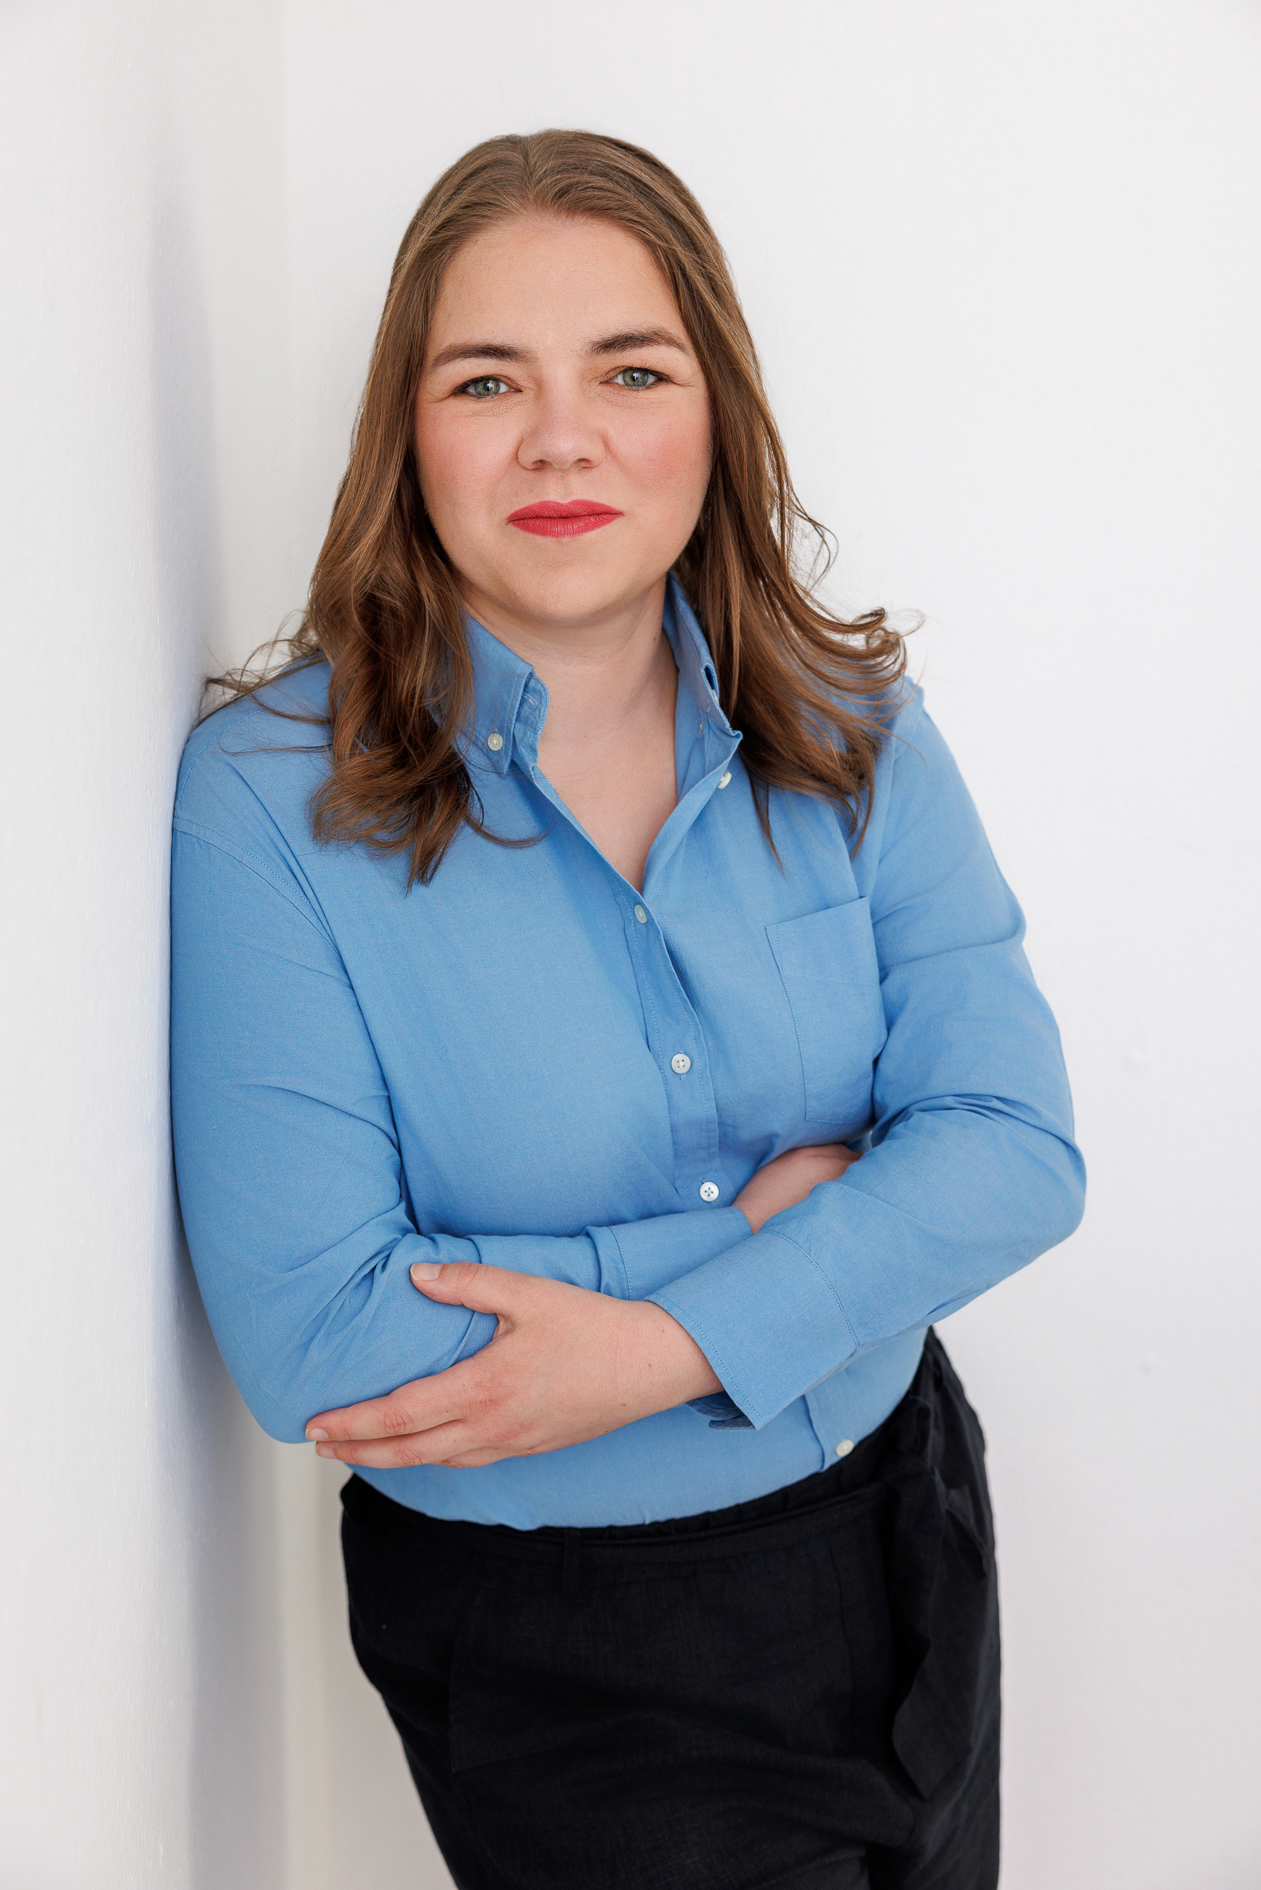
Your Accountability Partner:
Carolin Desirée Toepfer
As external Chief Information Security Officer and IT Forensics Specialist, I help organizations build a stronger cybersecurity posture, adopt AI securely, and turn complex risks into clear, actionable decisions.
My work sits at the intersection of Cybersecurity, AI Security, Risk Management, and Regulatory Compliance. I help organizations understand emerging cyber and AI risks, establish practical security structures, and implement secure AI solutions without slowing down innovation.
I sit at the table where the rules are written: as a member of several working groups, I collaborate directly with legal experts, representatives of highly regulated organizations, and relevant authorities. I translate complex regulatory and security requirements into practical, cost-efficient measures that strengthen resilience without creating unnecessary bureaucracy.
As an entrepreneur, I understand the reality behind the requirements. Security needs to work not only on paper, but in everyday operations, under time pressure, with real people, real budgets, and constantly changing technology. My goal is to enable organizations and their teams to make better security decisions every day.
My keynotes and trainings are popular with both executives and employees because I don't use fear to create awareness, and I don't create dependencies to sell security.
Curriculum
- How do Hackers look like? (2:55)
- Assets at Risk (1:16)
- From Computer Virus to AI Fraud (2:13)
- Work Process Attacks (1:55)
- Supply Chain Attacks
- AI Attacks (0:47)
- Attacks against Key Player (3:15)
- Identity Theft (2:06)
- AI Deepfakes (1:44)
- Reputation Damages (1:23)
- Proof of not being under Attack (1:07)
- No Legal Advice! But Guidance. (1:40)
- Regulatory Patterns (2:44)
- Data Protection (2:30)
- Cybersecurity (2:18)
- Business Continuity (1:20)
- Artificial Intelligence (0:50)
- Industry Requirements (0:40)
- Controlling Supply Chains (1:22)
- Reporting Timelines (3:08)
- Regulator's Platforms
- Checklist: Legal Meeting Prep
- Just for better overview - don't stress!
- How to set up your work environment for success: (6:46)
- Document Folder, Cybersecurity Inbox, Support Flows
- Checklist: Quick Fixes [Chapter 2]
- Checklist: Legal Meeting Prep [Chapter 3]
- PROJECT OVERVIEW TEMPLATE
- Training Plan Template [Chapter 6]
- Cybersecurity Frameworks & Vendor Management Templates [Chapter 7 & 12]
- Policies [Chapter 11]
Cybersecurity shouldn't be a guessing game!
Your clients are asking security questions.
Enterprise prospects want evidence.
Regulations are changing.
AI is creating new risks.
And you may not know:
- What do we actually need to protect?
- Which risks should we fix first?
- What policies and processes do we need?
- Are we ready for ISO 27001, CyberTrust or SOC 2?
- How do we answer customer security questionnaires?
- What happens if we suffer a cyber incident?