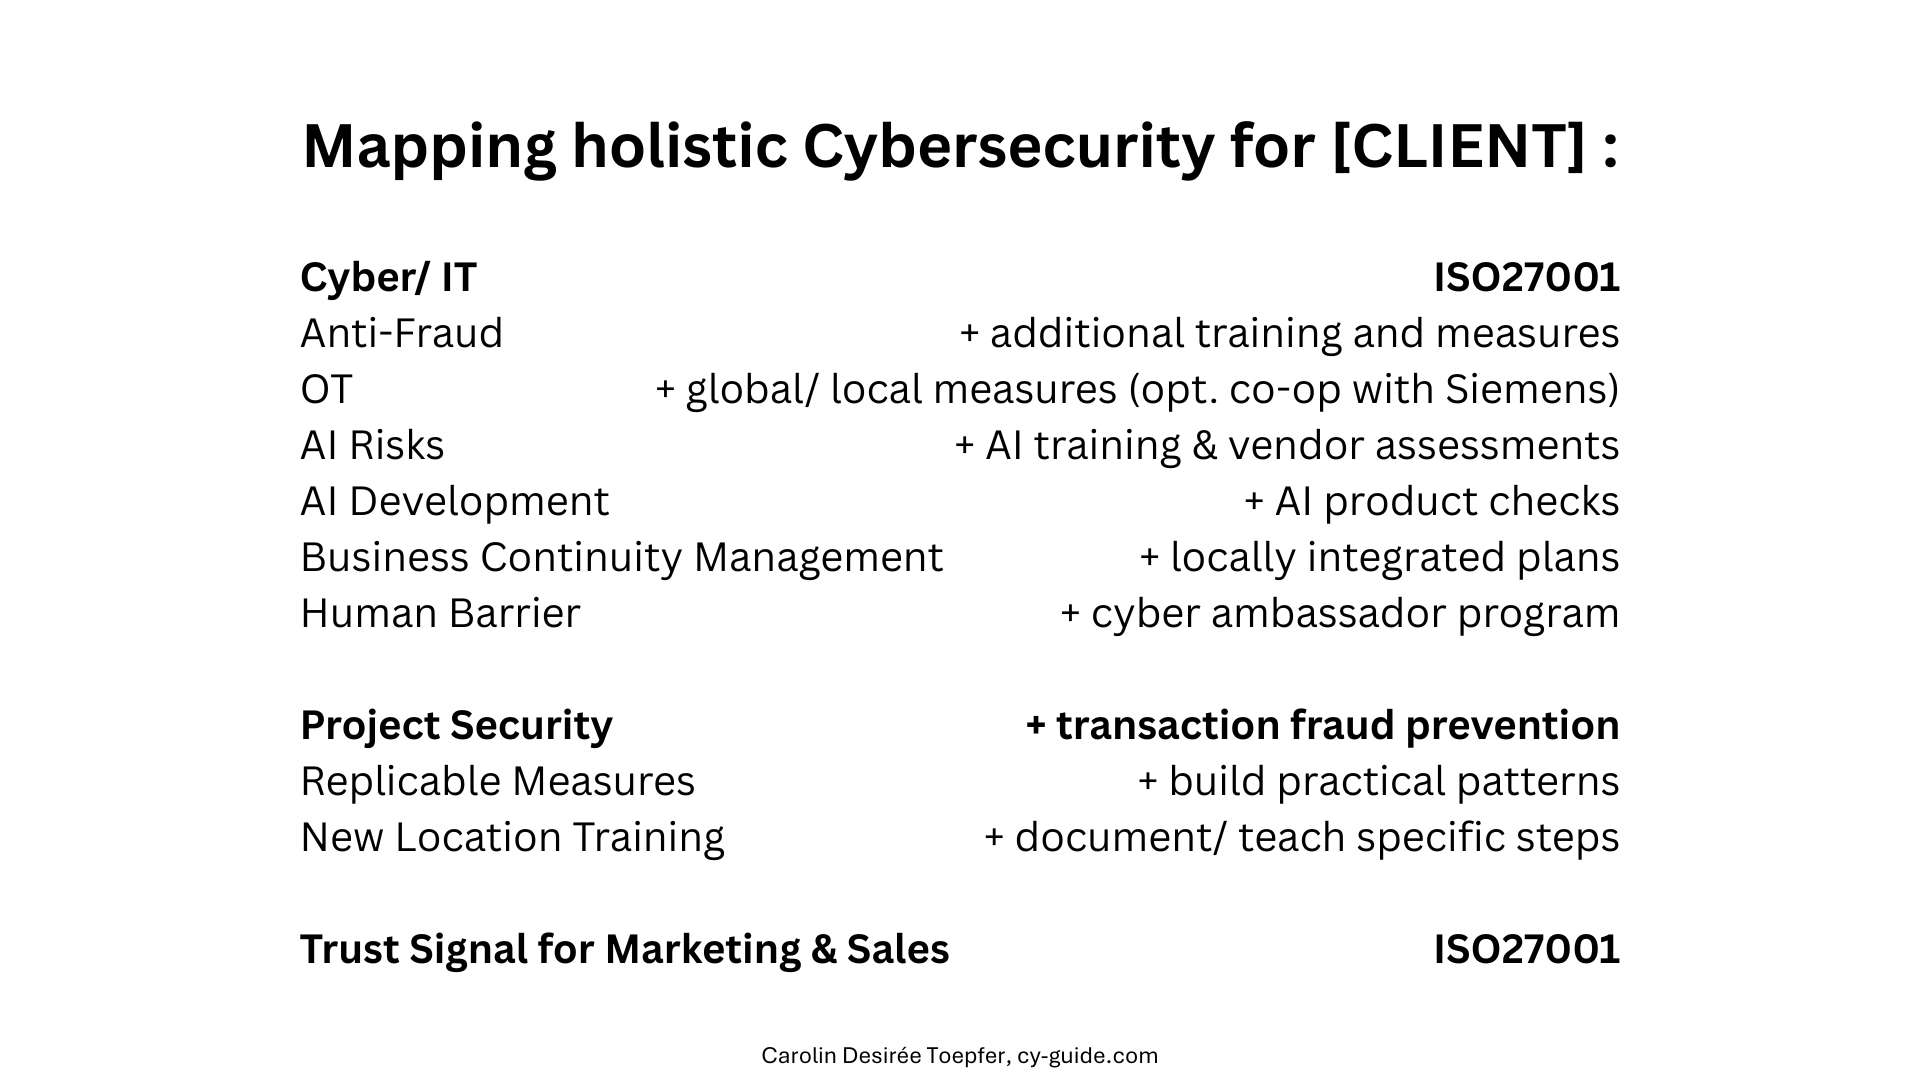
Attack Surface -> Protection Measures
Initial overview I created for a client with physical locations - and therefore OT/ operational technology setups - who also creates digital/ AI solutions.
As you can see, the pure implementation of a cybersecurity framework - in this case the ISO27001 - doesn't cover all the risks of the business model's attack surface and day to day operations. Same goes for regulatory frameworks - they are just not up to date (enough)!
Therefore, we need to have an eye on:
1. the global attack landscape (until yesterday; you get updates here);
2. the whole business and future planning, as well as
3. additional measures we integrate in our strategy
-> a holistic cybersecurity strategy, protecting the business now and in the future against real-world attack scenarios!
And as another layer or "parachute" we also prepare a worst case plan and business continuity strategy - before something goes wrong!